
NSE5_FSM-6.3 Braindumps PDF, Fortinet NSE5_FSM-6.3 Exam Cram
New 2026 NSE5_FSM-6.3 Sample Questions Reliable NSE5_FSM-6.3 Test Engine
NEW QUESTION # 20
Which process converts raw log data to structured data?
- A. Data classification
- B. Data validation
- C. Data enrichment
- D. Data parsing
Answer: D
Explanation:
* Raw Log Data: When devices send logs to FortiSIEM, the data arrives in a raw, unstructured format.
* Data Parsing Process: The process that converts this raw log data into a structured format is known as data parsing.
Data Parsing: This involves extracting relevant fields from the raw log entries and organizing them into a structured format, making the data usable for analysis, reporting, and correlation.
* Significance of Structured Data: Structured data is essential for effective event correlation, alerting, and generating meaningful reports.
* Reference: FortiSIEM 6.3 User Guide, Data Parsing section, which details how raw log data is transformed into structured data through parsing.
NEW QUESTION # 21
IF the reported packet loss is between 50% and 98%. which status is assigned to the device in the Availability column of summary dashboard?
- A. Down status is assigned because of packet loss.
- B. Up status is assigned because of received packets.
- C. Degraded status is assigned because of packet loss
- D. Critical status is assigned because of reduction in number of packets received.
Answer: C
Explanation:
* Device Status in FortiSIEM: FortiSIEM assigns different statuses to devices based on their operational state and performance metrics.
* Packet Loss Impact: The reported packet loss percentage directly influences the status assigned to a device. Packet loss between 50% and 98% indicates significant network issues that affect the device's performance.
* Degraded Status: When packet loss is between 50% and 98%, FortiSIEM assigns a "Degraded" status to the device. This status indicates that the device is experiencing substantial packet loss, which impairs its performance but does not render it completely non-functional.
* Reasoning: The "Degraded" status helps administrators identify devices with serious performance issues that need attention but are not entirely down.
* Reference: FortiSIEM 6.3 User Guide, Device Availability and Status section, explains the criteria for assigning different statuses based on performance metrics such as packet loss.
NEW QUESTION # 22
Which process convertsRaw log data to structured data?
- A. Data classification
- B. Data validation
- C. Data enrichment
- D. Data parsing
Answer: D
NEW QUESTION # 23
Which FortiSIEM components can do performance availability and performance monitoring?
- A. Supervisor, worker, and collector
- B. Collectors only
- C. Supervisor and workers only
- D. Supervisor only
Answer: A
Explanation:
* Performance and Availability Monitoring: Various components in FortiSIEM are responsible for monitoring the performance and availability of devices and services.
* Components:
Supervisor: Oversees the entire FortiSIEM infrastructure and coordinates the activities of other components.
Worker: Processes and analyzes the collected data, including performance and availability metrics.
Collector: Gathers performance and availability data from devices in the network.
* Collaborative Functioning: These components work together to ensure comprehensive monitoring of the network's performance and availability.
* Reference: FortiSIEM 6.3 User Guide, Performance and Availability Monitoring section, which explains the roles of the supervisor, worker, and collector in monitoring tasks.
NEW QUESTION # 24
Which database is used for storing anomaly data, that is calculated for different parameters, such as traffic and device resource usage running averages, and standard deviation values?
- A. SVN DB
- B. Profile DB
- C. CMDB
- D. Event DB
Answer: B
Explanation:
* Anomaly Data Storage: Anomaly data, including running averages and standard deviation values for different parameters such as traffic and device resource usage, is stored in a specific database.
* Profile DB: The Profile DB is used to store this type of anomaly data.
Function: It maintains statistical profiles and baselines for monitored parameters, which are used to detect anomalies and deviations from normal behavior.
* Significance: Storing anomaly data in the Profile DB allows FortiSIEM to perform advanced analytics and alerting based on deviations from established baselines.
* Reference: FortiSIEM 6.3 User Guide, Database Architecture section, which describes the purpose and contents of the Profile DB in storing anomaly and baseline data.
NEW QUESTION # 25
Which FortiSIEM components are capable of performing device discovery?
- A. FortiSIEM Windows agent
- B. Worker
- C. Collector
- D. FortiSIEM Linux agent
Answer: C
NEW QUESTION # 26
In the CMDB page for a network device, the Configuration tab is unexpectedly empty. Which is a possible reason?
- A. A Telnet/SSH credential was not configured for discovery.
- B. The SNMP credential was a read-only credential.
- C. Syslog was only being sent to a worker.
- D. Configuration push is not enabled on the network device.
Answer: A
NEW QUESTION # 27
IF the reported packet loss is between 50% and 98%. which status is assigned to the device in the Availability column of summary dashboard?
- A. Down status is assigned because of packet loss.
- B. Up status is assigned because of received packets.
- C. Critical status is assigned because of reduction in number of packets received.
- D. Degraded status is assigned because of packet loss
Answer: C
Explanation:
Device Status in FortiSIEM: FortiSIEM assigns different statuses to devices based on their operational state and performance metrics.
Packet Loss Impact: The reported packet loss percentage directly influences the status assigned to a device.
Packet loss between 50% and 98% indicates significant network issues that affect the device's performance.
Degraded Status: When packet loss is between 50% and 98%, FortiSIEM assigns a "Degraded" status to the device. This status indicates that the device is experiencing substantial packet loss, which impairs its performance but does not render it completely non-functional.
Reasoning: The "Degraded" status helps administrators identify devices with serious performance issues that need attention but are not entirely down.
References: FortiSIEM 6.3 User Guide, Device Availability and Status section, explains the criteria for assigning different statuses based on performance metrics such as packet loss.
NEW QUESTION # 28
Refer to the exhibit.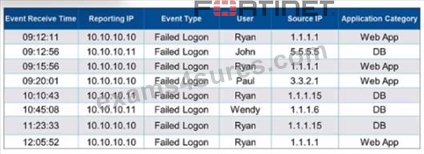
It events are grouped by Event Type and User attributes in FortiSIEM. how many results will be displayed?
- A. Four results will be displayed.
- B. Eight results will be displayed.
- C. No results will be displayed.
- D. Two results will be displayed.
Answer: B
Explanation:
* Grouping Events in FortiSIEM: Grouping events by specific attributes allows administrators to aggregate and analyze data more efficiently.
* Grouping Criteria: In this case, the events are grouped by "Event Type" and "User" attributes.
* Unique Combinations: To determine the number of results displayed, identify the unique combinations of the "Event Type" and "User" attributes in the provided data.
Failed Logon by Ryan (appears multiple times but is one unique combination) Failed Logon by John Failed Logon by Paul Failed Logon by Wendy
* Unique Groupings: There are four unique groupings based on the given data: "Failed Logon" by "Ryan", "John", "Paul", and "Wendy".
* Reference: FortiSIEM 6.3 User Guide, Event Management and Reporting sections, which explain how events are grouped and reported based on selected attributes.
NEW QUESTION # 29
Device discovery information is stored in which database?
- A. SVN DB
- B. Profile DB
- C. Event DB
- D. CMDB
Answer: D
Explanation:
Device Discovery Information: Information about discovered devices, including their configurations and statuses, is stored in a specific database.
CMDB: The Configuration Management Database (CMDB) is used to store detailed information about the devices discovered by FortiSIEM.
* Function: It maintains comprehensive details about device configurations, relationships, and other metadata essential for managing the IT infrastructure.
Significance: Storing discovery information in the CMDB ensures that the FortiSIEM system has a centralized repository of device information, facilitating efficient management and monitoring.
References: FortiSIEM 6.3 User Guide, Configuration Management Database (CMDB) section, which details the storage and usage of device discovery information.
NEW QUESTION # 30
Refer to the exhibit.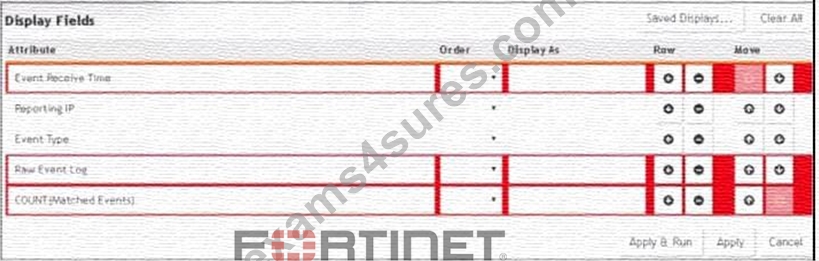
A FortiSIEM administrator wants to group some attributes for a report, but is not able to do so successfully.
As shown in the exhibit, why are some of the fields highlighted in red?
- A. Unique attributes cannot be grouped.
- B. The Event Receive Time attribute is not available for logs.
- C. No RAW Event Log attribute is available for devices.
- D. The attribute COUNT(Matched events) is an invalid expression.
Answer: A
Explanation:
Grouping Attributes in Reports: When creating reports in FortiSIEM, certain attributes can be grouped to summarize and organize the data.
Unique Attributes: Attributes that are unique for each event cannot be grouped because they do not provide a meaningful aggregation or summary.
Red Highlighting Explanation: The red highlighting in the exhibit indicates attributes that cannot be grouped together due to their unique nature. These unique attributes includeEvent Receive Time,Reporting IP,Event Type,Raw Event Log, andCOUNT(Matched Events).
Attribute Characteristics:
* Event Receive Timeis unique for each event.
* Reporting IPandEvent Typecan vary greatly, making grouping them impractical in this context.
* Raw Event Logrepresents the unprocessed log data, which is also unique.
* COUNT(Matched Events)is a calculated field, not suitable for grouping.
References: FortiSIEM 6.3 User Guide, Reporting section, explains the constraints on grouping attributes in reports.
NEW QUESTION # 31
In FortiSIEM enterprise licensing mode, it the link between the collector and data center FortiSlEM cluster is down, what happens?
- A. The collector processes stop, and events ate dropped.
- B. The collector buffers events
- C. The collector drops incoming events like syslog. but stops performance collection.
- D. The collector continues performance collection of devices, but slops receiving syslog.
Answer: D
Explanation:
* Enterprise Licensing Mode: In FortiSIEM enterprise licensing mode, collectors are deployed in remote sites to gather and forward data to the central FortiSIEM cluster located in the data center.
* Collector Functionality: Collectors are responsible for receiving logs, events (e.g., syslog), and performance metrics from devices.
* Link Down Scenario: When the link between the collector and the FortiSIEM cluster is down, the collector needs a mechanism to ensure no data is lost during the disconnection.
* Event Buffering: The collector buffers the events locally until the connection is restored, ensuring that no incoming events are lost. This buffered data is then forwarded to the FortiSIEM cluster once the link is re-established.
* Reference: FortiSIEM 6.3 User Guide, Data Collection and Buffering section, explains the behavior of collectors during network disruptions.
NEW QUESTION # 32
Refer to the exhibit.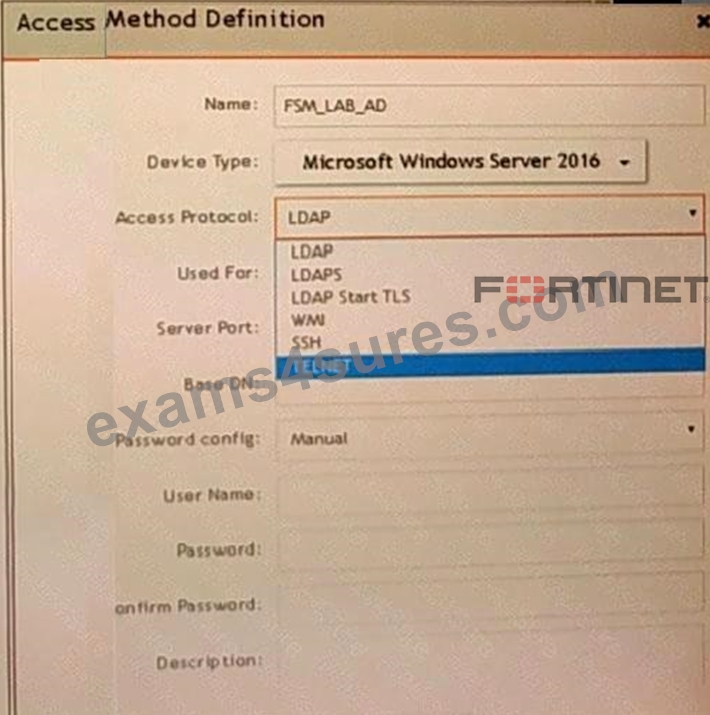
A FortiSIEM administrator wants to collect both SIEM event logs and performance and availability metrics (PAM) events from a Microsoft Windows server Which protocol should the administrator select in the Access Protocol drop-down list so that FortiSIEM will collect both SIEM and PAM events?
- A. LDAP start TLS
- B. WMI
- C. TELNET
- D. LDAPS
Answer: B
Explanation:
Collecting SIEM and PAM Events: To collect both SIEM event logs and Performance and Availability Monitoring (PAM) events from a Microsoft Windows server, a suitable protocol must be selected.
WMI Protocol: Windows Management Instrumentation (WMI) is the appropriate protocol for this task.
* SIEM Event Logs: WMI can collect security, application, and system logs from Windows devices.
* PAM Events: WMI can also gather performance metrics, such as CPU usage, memory utilization, and disk activity.
Comprehensive Data Collection: Using WMI ensures that both types of data are collected efficiently from the Windows server.
References: FortiSIEM 6.3 User Guide, Data Collection Methods section, which details the use of WMI for collecting various types of logs and performance metrics.
NEW QUESTION # 33
How is a subpattern for a rule defined?
- A. Filters, Aggregation, Time Window definitions
- B. Filters, Aggregation, Group by definitions
- C. Filters, Group By definitions, Threshold
- D. Filters, Threshold, Time Window definitions
Answer: D
NEW QUESTION # 34
An administrator defines SMTP as a critical process on a Linux server.
It the SMTP process is stopped. FortiSIEM will generate a critical event with which event type?
- A. PH_DEV_MON_SMTP_STOP
- B. Postfix-Mail-Stop
- C. Generic_SMTP_Procoss_Exit
- D. PH_DEV_MON_PROC_STOP
Answer: D
Explanation:
* Process Monitoring in FortiSIEM: FortiSIEM can monitor critical processes on managed devices, such as an SMTP process on a Linux server.
* Event Generation: When a critical process stops, FortiSIEM generates an event to alert administrators.
* Event Types: Specific event types correspond to different monitored conditions. For a stopped process, the event type PH_DEV_MON_PROC_STOP is used.
* Reasoning: The name PH_DEV_MON_PROC_STOP (Device Monitoring Process Stop) is a generic event type used by FortiSIEM to indicate that any monitored process, including SMTP, has stopped.
* Reference: FortiSIEM 6.3 User Guide, Event Types section, explains the predefined event types and their usage in different monitoring scenarios.
NEW QUESTION # 35
Which FortiSIEM feature must you use to produce a report on which FortiGate devices in your environment are running which firmware version?
- A. Run a CMDB report
- B. Run a baseline report.
- C. Run a query using the Inventory tab.
- D. Run an analytic search.
Answer: C
Explanation:
* Feature Overview: FortiSIEM provides several tools for querying and reporting on device information within an environment.
* Inventory Tab: The Inventory tab is specifically designed to display detailed information about devices, including their firmware versions.
* Query Functionality: Within the Inventory tab, you can run queries to filter and display devices based on specific attributes, such as the firmware version for FortiGate devices.
* Report Generation: By running a query in the Inventory tab, you can produce a report that lists the FortiGate devices and their corresponding firmware versions.
* Reference: FortiSIEM 6.3 User Guide, Inventory Management section, explains how to use the Inventory tab to query and report on device attributes.
NEW QUESTION # 36
......
Feel Fortinet NSE5_FSM-6.3 Dumps PDF Will likely be The best Option: https://www.exams4sures.com/Fortinet/NSE5_FSM-6.3-practice-exam-dumps.html
NSE5_FSM-6.3 exam torrent Fortinet study guide: https://drive.google.com/open?id=1o4VCQR1zcMQftSJ_RydSYcjzd4gD8DiI