
CompTIA CS0-002 Test Engine Practice Test Questions, Exam Dumps
100% Free CS0-002 Daily Practice Exam With 371 Questions
Earning the CompTIA CySA+ certification demonstrates to employers and clients that the IT professional possesses the necessary skills and knowledge to protect an organization's systems and data from cyber attacks. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is highly valued by organizations and is an excellent way to advance your career in the cybersecurity field.
NEW QUESTION # 150
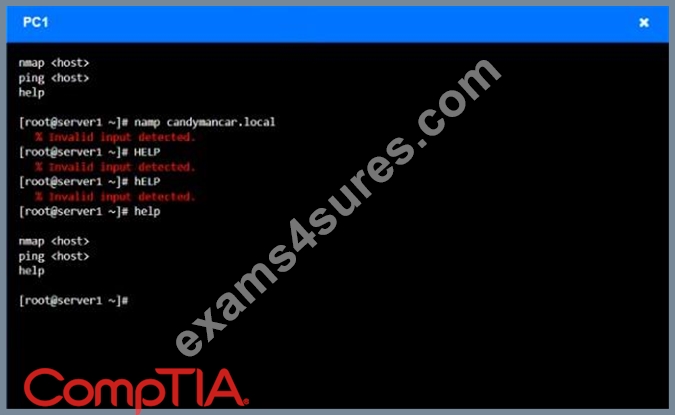
You are a penetration tester who is reviewing the system hardening guidelines for a company. Hardening guidelines indicate the following.
There must be one primary server or service per device.
Only default port should be used
Non- secure protocols should be disabled.
The corporate internet presence should be placed in a protected subnet
Instructions :
Using the available tools, discover devices on the corporate network and the services running on these devices.
You must determine
ip address of each device
The primary server or service each device
The protocols that should be disabled based on the hardening guidelines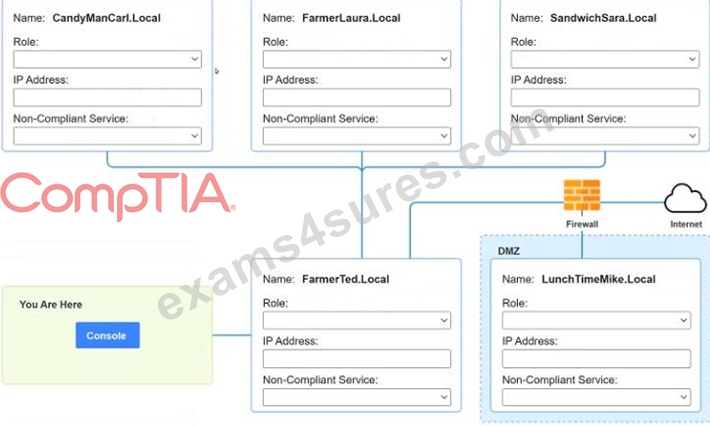
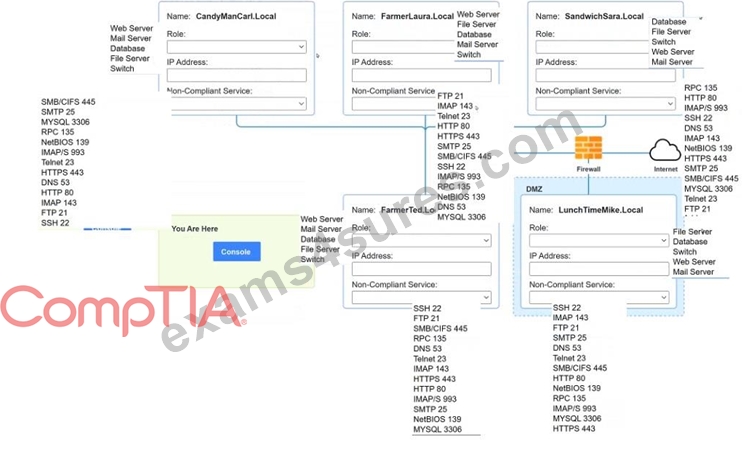
- A. see the answer below in explanation
Answer: A
Explanation:
Answer below images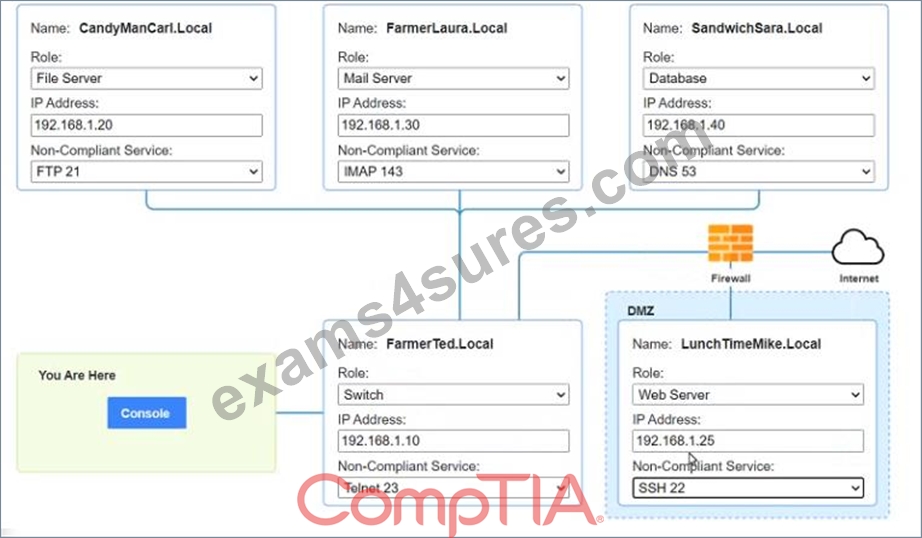
NEW QUESTION # 151
A security analyst is attempting to utilize the blowing threat intelligence for developing detection capabilities:
In which of the following phases is this APT MOST likely to leave discoverable artifacts?
- A. Reconnaissance
- B. Data collection/exfiltration
- C. Lateral movement
- D. Defensive evasion
Answer: B
NEW QUESTION # 152
A zero-day crypto-worm is quickly spreading through the internal network on port 25 and exploiting a software vulnerability found within the email servers. Which of the following countermeasures needs to be implemented as soon as possible to mitigate the worm from continuing to spread?
- A. Isolate impacted servers.
- B. Implement a traffic sinkhole.
- C. Patch affected systems.
- D. Block all known port/services.
Answer: A
NEW QUESTION # 153
After receiving reports latency, a security analyst performs an Nmap scan and observes the following output:
Which of the following suggests the system that produced output was compromised?
- A. MySQL services is identified on a standard PostgreSQL port.
- B. There are no indicators of compromise on this system.
- C. Secure shell is operating of compromise on this system.
- D. Standard HTP is open on the system and should be closed.
Answer: B
NEW QUESTION # 154
A security analyst reviews SIEM logs and detects a well-known malicious executable running in a Windows machine The up-to-date antivirus cannot detect the malicious executable Which of the following is the MOST likely cause of this issue?
- A. The antivirus does not have the mltware's signature.
- B. The malware is being executed with administrative privileges.
- C. The malware is fileless and exists only in physical memory.
- D. The malware detects and prevents its own execution in a virtual environment.
Answer: C
NEW QUESTION # 155
Industry partners from critical infrastructure organizations were victims of attacks on their SCADA devices.
The attacker was able to gain access to the SCADA by logging in to an account with weak credentials. Which of the following identity and access management solutions would help to mitigate this risk?
- A. Multifactor authentication
- B. Role-based access control
- C. Endpoint detection and response
- D. Manual access reviews
Answer: B
Explanation:
Explanation
RBAC helps organizations manage access to critical infrastructure networks by assigning access based on roles. This allows organizations to control who can access specific resources and helps eliminate weak credentials that attackers could exploit. Manual reviews and endpoint detection and response can also help to mitigate risk, but role based access control is the best solution for this scenario.
NEW QUESTION # 156
A security analyst reviews the latest reports from the company's vulnerability scanner and discovers the following: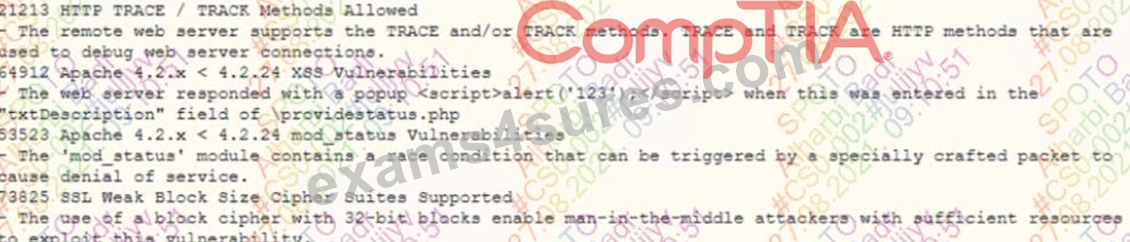
Which of the following changes should the analyst recommend FIRST?
- A. Configuring SSL ciphers to use different encryption blocks
- B. Programming changes to encode output
- C. Disabling HTTP connection debugging commands
- D. Updating the 'mod_status' module
Answer: D
NEW QUESTION # 157
Which of the following ICS network protocols has no inherent security functions on TCP port 502?
- A. SSH
- B. DHCP
- C. CIP
- D. Modbus
Answer: D
Explanation:
Modbus is an industrial control system (ICS) network protocol that is used for communication between devices such as sensors, controllers, actuators, and monitors. Modbus has no inherent security functions on TCP port 502, which is the default port for Modbus TCP/IP communication. Modbus does not provide any encryption, authentication, or integrity protection for the data transmitted over the network, making it vulnerable to various attacks such as replay, modification, spoofing, or denial-of-service.
NEW QUESTION # 158
Which of the following BEST describes how logging and monitoring work when entering into a public cloud relationship with a service provider?
- A. Logging and monitoring are done by the service provider
- B. Logging and monitoring are not needed in a public cloud environment
- C. Logging and monitoring duties are specified in the SLA and contract
- D. Logging and monitoring are done by the data owners
Answer: A
Explanation:
Explanation
When transitioning over to a cloud solution, an organization may lose visibility of certain points on the technology stack, particularly if it's subscribing to PaaS or SaaS solutions. Because the responsibility of protecting portions of the stack falls to the service provider, it does sometimes mean the organization loses monitoring capabilities, for better or worse. Chapman, Brent; Maymi, Fernando. CompTIA CySA+ Cybersecurity Analyst Certification All-in-One Exam Guide, Second Edition (Exam CS0-002) (p. 158).
McGraw Hill LLC. Kindle Edition.
NEW QUESTION # 159
A security analyst is investigating malicious traffic from an internal system that attempted to download proxy avoidance software as identified from the firewall logs but the destination IP is blocked and not captured.
Which of the following should the analyst do?
- A. Review the network logs.
- B. Take a snapshot
- C. Shut down the computer
- D. Determine if DNS logging is enabled.
- E. Capture live data using Wireshark
Answer: C
NEW QUESTION # 160
An organization is conducting penetration testing to identify possible network vulnerabilities. The penetration tester has received the following output from the latest scan: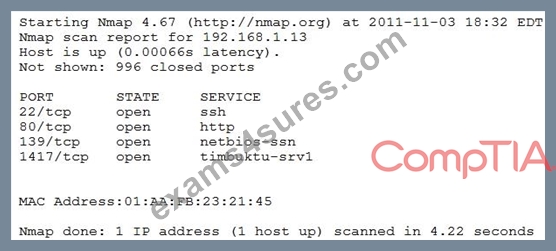
The penetration tester knows the organization does not use Timbuktu servers and wants to have Nmap interrogate the ports on the target in more detail. Which of the following commands should the penetration tester use NEXT?
- A. nmap -sV 192.168.1.13 -p1417
- B. sudo nmap -sS 192.168.1.13
- C. nmap -sS 192.168.1.13 -p1417
- D. nmap 192.168.1.13 -v
Answer: A
NEW QUESTION # 161
An analyst Is reviewing a web developer's workstation for potential compromise. While examining the workstation's hosts file, the analyst observes the following: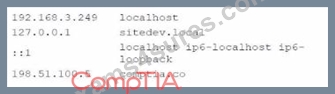
Which of the following hosts file entries should the analyst use for further investigation?
- A. 127.0.0.1
- B. ::1
- C. 198.51.100.5
- D. 192.168.3.249
Answer: C
Explanation:
The hosts file is a text file that maps hostnames to IP addresses, and it can be used to override DNS resolution. The hosts file entries that should be used for further investigation are the ones that point to external or suspicious IP addresses, such as 198.51.100.5, which is a reserved IP address for documentation purposes. The other entries are either loopback addresses (::1 and 127.0.0.1) or internal network addresses (192.168.3.249), which are less likely to be malicious.
NEW QUESTION # 162
An organization wants to mitigate against risks associated with network reconnaissance. ICMP is already blocked at the firewall; however, a penetration testing team has been able to perform reconnaissance against the organization's network and identify active hosts. An analyst sees the following output from a packet capture:
Which of the following phrases from the output provides information on how the testing team is successfully getting around the ICMP firewall rule?
- A. flags=RA indicates the testing team is using a Christmas tree attack
- B. 0 data bytes indicates the testing team is crafting empty ICMP packets
- C. NO FLAGS are set indicates the testing team is using hping
- D. ttl=64 indicates the testing team is setting the time to live below the firewall's threshold
Answer: C
NEW QUESTION # 163
Scan results identify critical Apache vulnerabilities on a company's web servers. A security analyst believes many of these results are false positives because the web environment mostly consists of Windows servers.
Which of the following is the BEST method of verifying the scan results?
- A. Perform a top-ports scan against the identified servers.
- B. Refer to the identified servers in the asset inventory.
- C. Run a service discovery scan on the identified servers.
- D. Review logs of each host in the SIEM.
Answer: C
NEW QUESTION # 164
A security analyst is reviewing a new Internet portal that will be used for corporate employees to obtain their pay statements. Corporate policy classifies pay statement information as confidential, and it must be protected by MFA. Which of the following would best fulfill the MFA requirement while keeping the portal accessible from the internet?
- A. Moving the internet portal server to a DMZ that is only accessible from the corporate VPN and requiring a username and password
- B. Requiring the internet portal to be accessible from only the corporate SSO internet endpoint and requiring a smart card and PIN
- C. Distributing a shared password that must be provided before the internet portal loads and requiring a username and password
- D. Obtaining home public IP addresses of corporate employees to implement source IP restrictions and requiring a username and password
Answer: B
Explanation:
Requiring the internet portal to be accessible from only the corporate SSO internet endpoint and requiring a smart card and PIN. This option provides the best MFA requirement because it uses two factors of authentication: something you have (smart card) and something you know (PIN). It also restricts access to the portal from a trusted source (corporate SSO internet endpoint).
NEW QUESTION # 165
A company is moving from the use of web servers hosted in an internal datacenter to a containerized cloud platform. An analyst has been asked to identify indicators of compromise in the containerized environment. Which of the following would BEST indicate a running container has been compromised?
- A. An approved software orchestration container is running with root privileges
- B. A container from an approved software image has drifted
- C. A container from an approved software image fails to start
- D. A container from an approved software image has stopped responding
Answer: B
NEW QUESTION # 166
Which of the following are considered PII by themselves? (Select TWO).
- A. Employer address
- B. Government ID
- C. Birth certificate
- D. Employment start date
- E. Job title
- F. Mother's maiden name
Answer: B,C
NEW QUESTION # 167
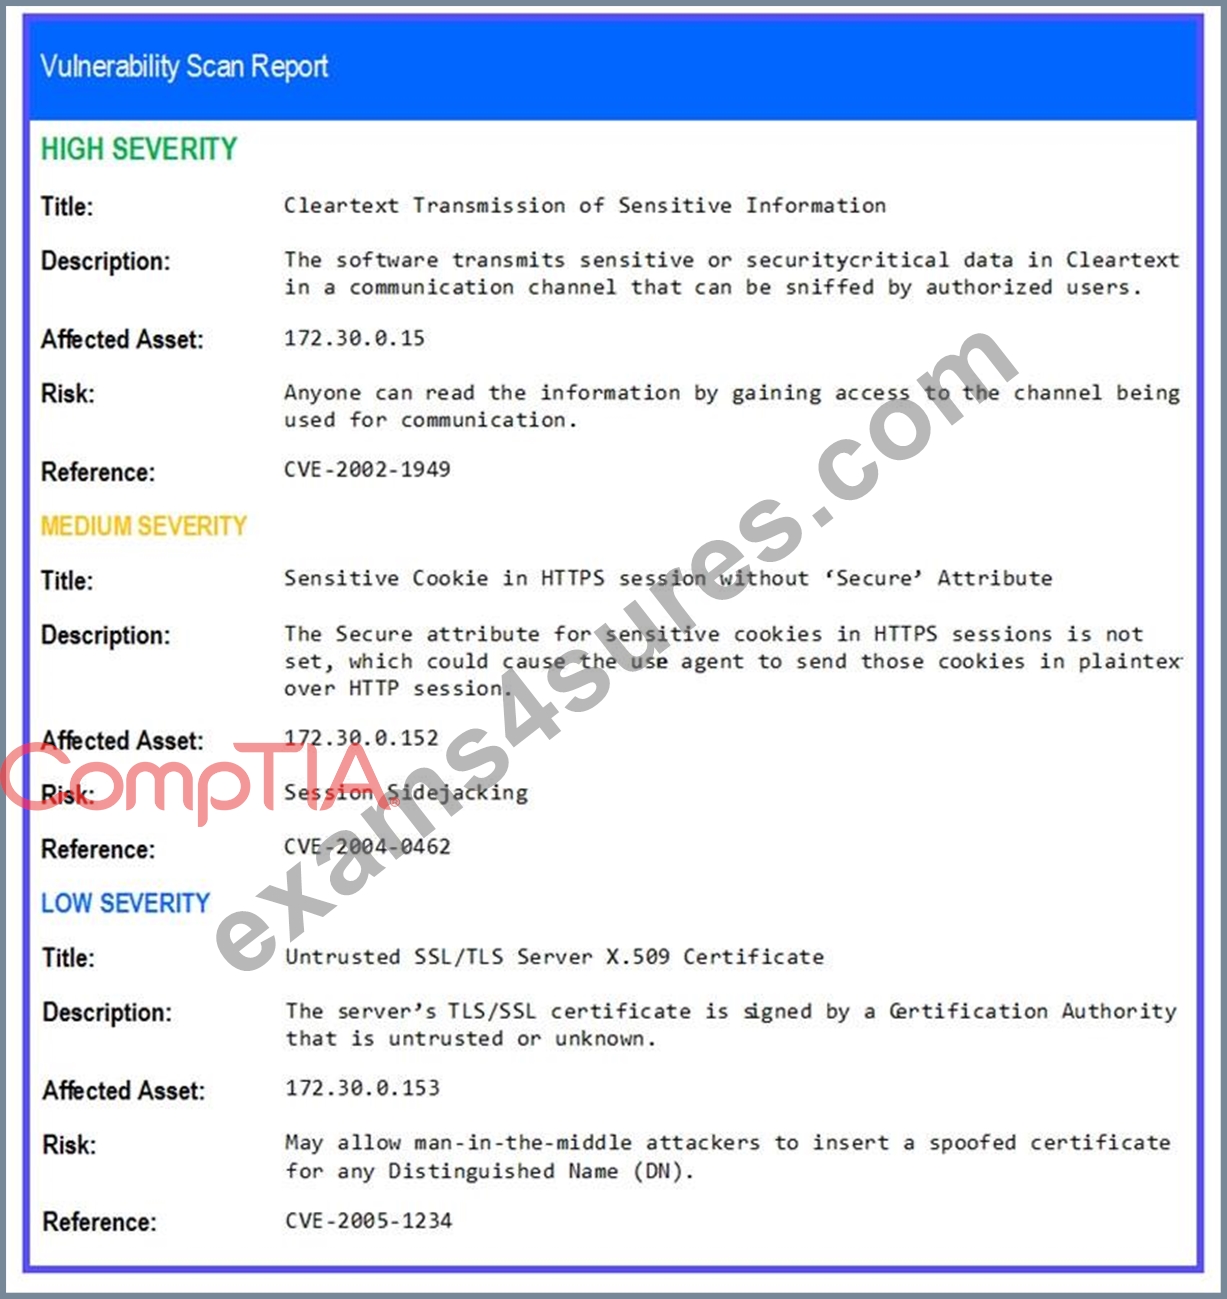
The developers recently deployed new code to three web servers. A daffy automated external device scan report shows server vulnerabilities that are failure items according to PCI DSS.
If the venerability is not valid, the analyst must take the proper steps to get the scan clean.
If the venerability is valid, the analyst must remediate the finding.
After reviewing the information provided in the network diagram, select the STEP 2 tab to complete the simulation by selecting the correct Validation Result and Remediation Action for each server listed using the drop-down options.
INTRUCTIONS:
The simulation includes 2 steps.
Step1:Review the information provided in the network diagram and then move to the STEP 2 tab.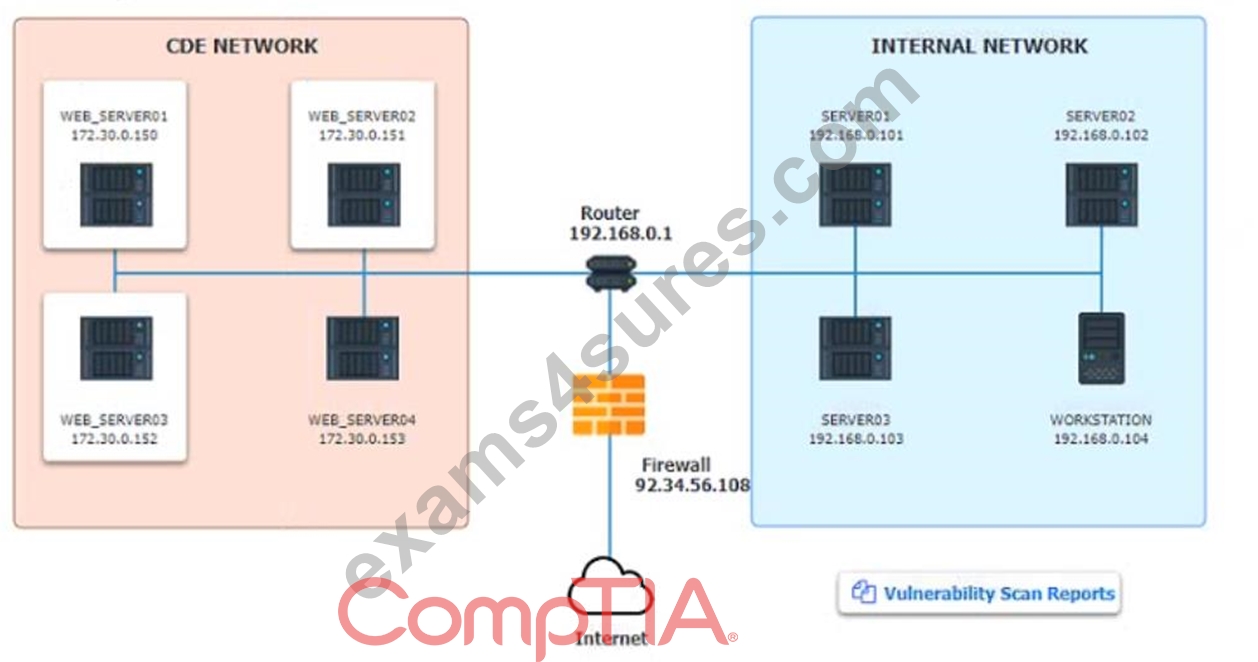
STEP 2: Given the Scenario, determine which remediation action is required to address the vulnerability.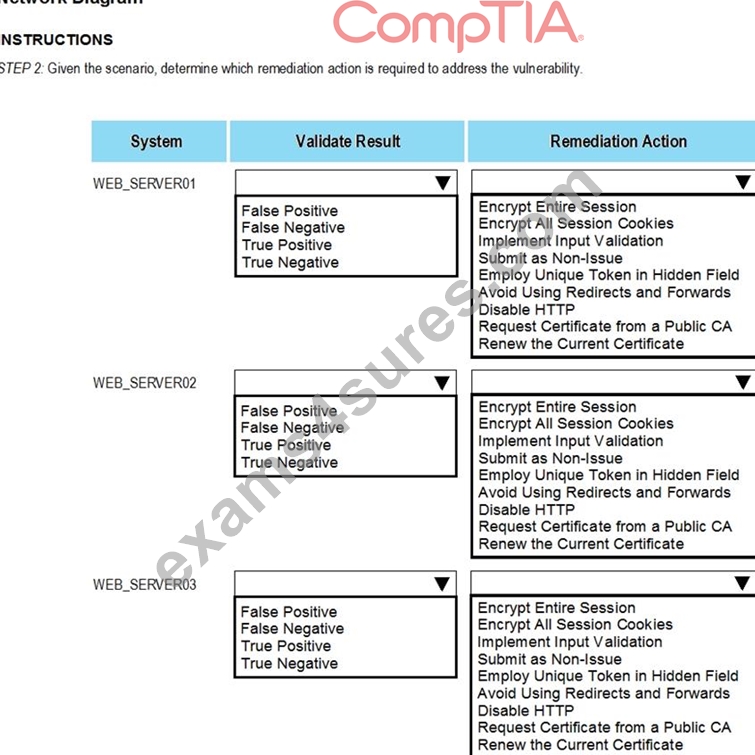
Answer:
Explanation: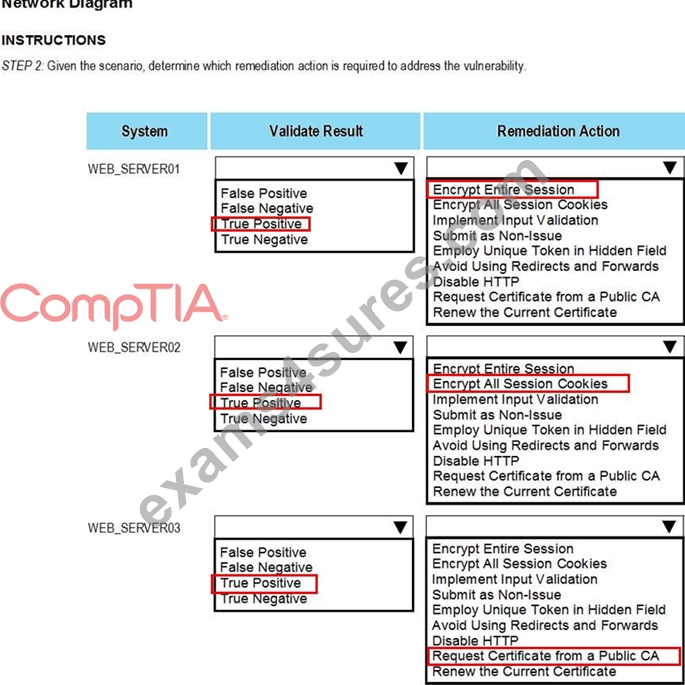
NEW QUESTION # 168
......
What can you expect after completing CompTIA CS0-002 exam?
The certified professionals can take up the job roles of a Security Analyst, a Security Engineer, an Incident Handler, a Threat Hunter, a Compliance Analyst, an Application Security Analyst, and a Threat Intelligence Analyst. The salary outlook for these positions is an average of $94,500 per annum. An experience level and specific job title will determine the actual remuneration that an individual can earn.
Use Valid New CS0-002 Test Notes & CS0-002 Valid Exam Guide: https://www.exams4sures.com/CompTIA/CS0-002-practice-exam-dumps.html
CS0-002 exam torrent CompTIA study guide: https://drive.google.com/open?id=1o_Hu2RF-JufN4kSPxCgziKR9Kr7PdOtX